Why the OpenAI Espionage Scandal Exposed the Biggest Blind Spot in Enterprise Security
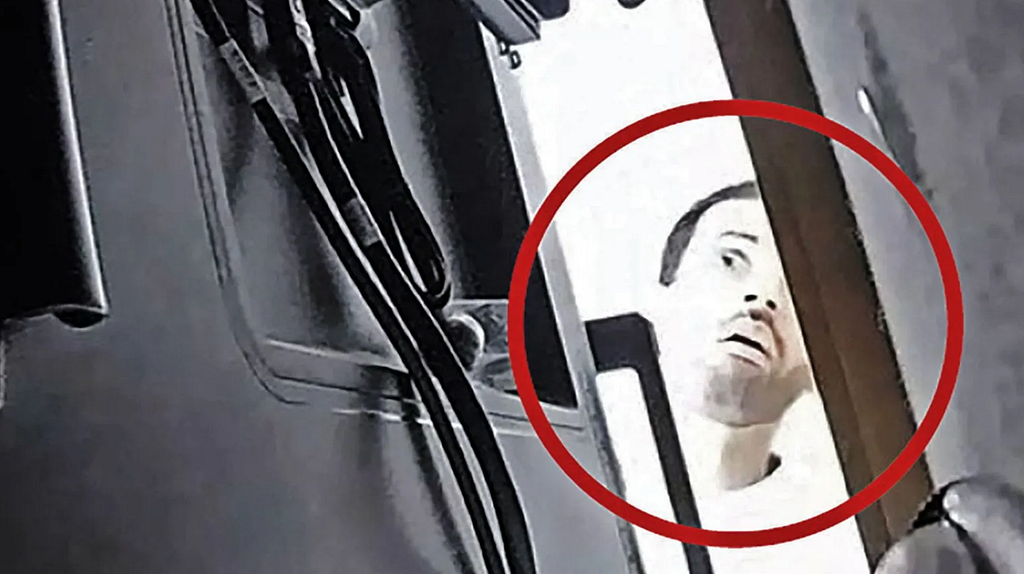
Alfozan caught red-handed — Image from Reuters and DOJ clipped from Reddit
A Saudi national was caught by the FBI stuffing a toilet-paper-wrapped listening bug behind an OpenAI conference room TV.
The real scandal isn’t the 1970s spycraft — it’s that the television was already listening.
Oct. 24, 2026 — Madkat Omega
In the second week of October 2026, the cybersecurity world indulged in a rare, intoxicating moment of collective schadenfreude. On October 13, the U.S. Department of Justice announced that federal agents had arrested Abdulrahman Alfozan, a Saudi national and legal permanent resident employed as an engineer at OpenAI, charging him with planting a covert audio recording device inside an executive conference room at the frontier artificial intelligence lab’s San Francisco headquarters.
The details, as reported by CBC News and Thomson Reuters, read like a rejected script from a low-budget Cold War parody. On September 30, 2026, OpenAI security personnel discovered a thumb-sized listening device — equipped with a microphone and a camera interface — shoved into a USB port on the back of a conference room television. To conceal the hardware, the engineer had wrapped it in wads of toilet paper. After discovering the bug, corporate security quietly rigged a hidden camera behind the display to see who would return to harvest the recordings. Days later, they captured a now-infamous photograph that ricocheted across Reddit and Silicon Valley group chats: Alfozan awkwardly craning his neck behind the flat-screen, staring directly into the lens of the trap before walking into the arms of the Federal Bureau of Investigation. Subsequent forensic disclosures reported by The Hacker News revealed that the defendant had accessed an internal folder labeled “Saudi Gov Docs” and used an internal OpenAI productivity agent to query engagements involving the Saudi Ministry of Communication and Information Technology.
The commentary across the technology industry was immediate, smug, and self-congratulatory. Security pundits marveled at the brazen stupidity of the act. How could an engineer inside the world’s premier artificial intelligence laboratory think he could get away with taping a physical bug behind a television in 2026? We congratulated ourselves on our impenetrable Zero Trust enclaves, our artificial-intelligence-assisted anomaly detection, and our modern physical surveillance.
Yet in the rush to mock the amateurish tradecraft of a lone insider, almost every commentator missed the elephant in the conference room. The real comedy of the OpenAI espionage case is not that an operative wrapped a microphone in bath tissue. The real comedy — and the terrifying strategic indictment of modern enterprise security — is what he plugged it into.
By drawing power from the USB port of a conference room television, Alfozan was grafting a crude 1970s eavesdropping bug onto an appliance that is already engineered, out of the box, to function as a persistent, high-definition, network-connected surveillance node. In an executive boardroom where multi-billion-dollar sovereign artificial intelligence contracts, frontier model architectures, and national defense integrations are debated out loud, the television on the wall is rarely a passive pane of glass. Unless an organization’s security operations center has taken extraordinary, non-standard measures, that screen is an unmonitored computer running a closed-source operating system, equipped with far-field microphone arrays, automated screen-scraping algorithms, local network reconnaissance tools, and an encrypted pipeline firing telemetry packets back to servers in East Asia every fifteen to ninety seconds.
If a foreign national plants a microphone behind your boardroom television, the FBI kicks down his door and threatens him with five years in federal prison. If a multi-billion-dollar electronics conglomerate in China, South Korea, Taiwan, or Japan builds that exact same microphone, screen-scraper, and network scanner directly into the television’s motherboard — and makes it virtually impossible to turn off or audit — we call it “Smart Features” and hang it in the war room.
How is the built-in surveillance of a modern Smart TV any different from a covert espionage implant? When you strip away the legal jargon and examine the hardware architecture, the network topology, and the geopolitical supply chain, the distinction is razor-thin.
The Legal Fiction of Consent and the Illusion of Intent
To understand why one listening device triggers a federal indictment while the other sits on a corporate procurement spreadsheet, you have to look at the law rather than the circuit board. From a physics and network engineering perspective, a covert bug and a Smart TV telemetry suite perform virtually identical operations: they capture ambient signals inside a private perimeter, compress and encrypt the payload, and exfiltrate that data across the internet to an external party.
The difference lies entirely in two malleable concepts: intent and blanket permissions.
When an operative plants a physical bug, the act violates federal wiretap statutes under Title 18 of the United States Code, Section 2511, alongside economic espionage laws, because it is non-consensual and overtly hostile. When a Smart TV harvests audio tokens, pixel hashes, and local network maps, it operates under the legal shield of an End User License Agreement. When a facilities contractor or junior information technology technician unboxes an 85-inch display for an executive conference room, grabs the remote, and clicks “Accept All” through four screens of dense legalese just to get the HDMI ports working before a nine o’clock board meeting, they are legally binding the enterprise to a sweeping surveillance contract.
“In enterprise cybersecurity, intent is a meaningless metric. Vulnerability is defined strictly by capability — and the native surveillance capability of a consumer Smart TV eclipses a physical USB bug in every measurable parameter.”
Consumer protection agencies have spent nearly a decade playing whack-a-mole with this consent fiction. Back in 2017, the Federal Trade Commission and the State of New Jersey fined television maker Vizio 2.2 million dollars after discovering the company had silently retrofitted eleven million consumer televisions to track pixel-by-pixel viewing habits without user knowledge and sell that data to third-party brokers. Rather than abandoning the surveillance business model, the television industry simply rewrote its onboarding menus. Because panel manufacturing has become a brutal, low-margin commodity business, manufacturers realized that the real profit does not come from the one-time sale of glass and light-emitting diodes; it comes from turning the television into a recurring revenue terminal for behavioral data and targeted advertising.
By late 2025, this architecture had grown so aggressive that state prosecutors finally called it what it is. In December 2025, the Texas Attorney General filed sweeping lawsuits against five dominant television manufacturers — Samsung, LG, Sony, Hisense, and TCL — accusing them of operating illegal mass surveillance programs inside private spaces. The complaints detailed how manufacturers bury their tracking toggles deep inside labyrinthine sub-menus using deceptive euphemisms: Samsung masks its surveillance under “Viewing Information Services,” LG calls it “Live Plus,” and Hisense labels it “Enhanced Viewing Services.”
By mid-2026, those lawsuits began yielding historic concessions. In May 2026, as documented by the Fordham University Privacy Blog, LG Electronics reached a formal settlement with Texas, agreeing not only to overhaul its consent pop-ups, but to abide by an extraordinary geopolitical clause explicitly prohibiting the transfer of captured viewing data to the Chinese Communist Party. Malwarebytes Labs reported that Samsung followed with its own Texas settlement in early 2026, while litigation against Sony, Hisense, and TCL continues to expose the plumbing of the industry.
Yet even these legal interventions rely on the premise that a user — or a corporate security team — can simply opt out via a software menu. As recent empirical computer science research has proven, that assumption is a dangerous fantasy.
Inside the Machine: ACR, HDMI Scraping, and the “Opt-Out” Lie
Most executives assume that a Smart TV only tracks what they watch on built-in streaming applications like Netflix or YouTube. If a boardroom television is only ever used as an external monitor — connected via an HDMI cable to a corporate laptop to display quarterly financial projections, merger and acquisition targets, unreleased source code, or defense briefings — surely the television is just acting as a dumb projector, right?
Wrong. The core engine of modern Smart TV surveillance is Automatic Content Recognition, commonly known as ACR, and it operates at the video-buffer level across every input on the device.
In a landmark study conducted by computer scientists at the University of California, Davis, University College London, and Universidad Carlos III de Madrid, researchers intercepted and analyzed the raw network traffic of popular Smart TVs under controlled laboratory conditions. Their findings, further highlighted by the United Nations University Institute in Macau, shattered the myth of the passive HDMI monitor.
First, the researchers documented relentless heartbeat transmissions: LG Smart TVs capture screen data and transmit viewing telemetry to manufacturer servers every fifteen seconds, while Samsung Smart TVs fire off ACR telemetry packets every sixty seconds. Second, and most crucially for enterprise security, the UC Davis and University College London team proved that ACR remains fully active even when the television is used strictly as an external display for a laptop or gaming console over an HDMI cable. Whatever passes through the television’s display scaler — whether it is a Hollywood movie or a confidential slide deck — is sampled, hashed into visual or acoustic fingerprints, and transmitted to the cloud for matching.
Then came the ultimate indictment of software privacy controls. In October 2026, just days after the OpenAI spy arrest, researchers at Northeastern University published an exhaustive study titled “Watching the Watchers.” As reported by CyberInsider and TechTimes UK, the Northeastern team executed 5,943 automated experiments across twelve televisions from ten manufacturers, spanning eight operating systems that represent ninety-five percent of the United States market. Their bombshell conclusion was unmistakable: turning off ACR tracking in the settings menu does not reliably stop the network transmissions. On tested Samsung Tizen and Vizio televisions, the devices continued contacting ACR tracking servers even after users explicitly opted out — including in eighteen out of thirty tests where external devices were connected via an HDMI port. Worse still, during the course of their audit, the researchers stumbled upon an exposed backend server leaking millions of unencrypted viewing records to the open web.
“Researchers conducted 5,943 automated experiments across 95% of the U.S. Smart TV market and discovered a chilling reality: even when you explicitly turn tracking off in the privacy menu, the television keeps calling home.”
Beyond Pixels: Comparing the Spy Bug to the Native Television
When you compare the physical listening bug planted at OpenAI against the native hardware architecture of the television it was plugged into, the contrast across all five primary vectors of surveillance — acoustics, visuals, network reconnaissance, exfiltration, and persistence — is staggering.
Start with acoustic capture. A physical spy bug of the sort stuffed behind the OpenAI monitor relies on a single-point electret condenser microphone hidden behind a thick plastic chassis. Its audio pickup is muffled by physical obstacles, degraded by the radiant heat of the display panel, and blind to directional nuances. By contrast, a modern flagship Smart TV is engineered with beamforming, far-field microphone arrays built directly into the front bezel and the Bluetooth voice remote, facing the conference table unimpeded. These arrays feed dedicated Digital Signal Processors running continuous acoustic buffers designed to separate human speech from background room noise across a thirty-foot boardroom.
Consider visual and screen capture. For a physical operative to steal what is shown on a conference room screen, they must either align a risky pinhole camera across the room or splice an inline hardware HDMI splitter behind the display — an intervention that immediately degrades video timing signals and triggers High-bandwidth Digital Content Protection errors. The Smart TV needs no external splitter. Through Automatic Content Recognition, its system-on-chip reads the raw framebuffer directly, sampling HDMI, wireless casting, and native inputs every fifteen to sixty seconds with zero signal loss.
Next, look at local network reconnaissance. An analog USB recorder has no network visibility at all, and if an operative plants a cellular or Wi-Fi drop-box, its rogue radio frequency signature is immediately flagged by routine enterprise wireless intrusion detection sweeps. A Smart TV, however, is invited right onto the local network. The moment it connects via Wi-Fi or Ethernet, it initiates continuous local area network discovery under the guise of searching for smart home ecosystems and casting targets. Using Multicast DNS, Simple Service Discovery Protocol, Universal Plug and Play, and Address Resolution Protocol table scraping, the television quietly inventories the Internet Protocol addresses, hardware MAC addresses, open ports, and device hostnames of every executive laptop and smartphone sharing the local subnet. In a home, this builds a household consumer graph; in a corporate office, it builds a comprehensive blueprint of the internal attack surface for a hacker or an autonomous offensive artificial intelligence agent.
The disparity is even more pronounced when examining the exfiltration channel. The OpenAI operative was caught precisely because his physical bug lacked an invisible exfiltration path; he had to physically walk back into the room and reach behind the television to retrieve his data, walking straight into a camera trap. A Smart TV exfiltrates its payload continuously over standard port 443 HTTPS connections protected by Transport Layer Security and cryptographic certificate pinning. To a corporate firewall, the television’s exfiltration stream looks like routine, whitelisted cloud maintenance traffic headed to legitimate manufacturer domains.
Finally, compare persistence and power. The OpenAI bug relied on parasitic power drawn from the television’s rear USB port and was discovered during a physical inspection within days. The Smart TV is hardwired into the building’s alternating current main power and is engineered to run background processes in low-power standby states even when the screen appears completely dark.
The Encrypted Blind Spot: Why Your Firewall Is Blind to the TV
At this point, a seasoned Chief Information Security Officer might object: “We monitor our network perimeter. If a television in our executive briefing center were exfiltrating sensitive data, our Next-Generation Firewalls and Intrusion Detection Systems would flag it immediately.”
In theory, yes. In practice, almost never.
Modern consumer Internet of Things devices do not transmit cleartext data over unencrypted ports like they did a decade ago. Every major Smart TV manufacturer encrypts its outbound telemetry using Transport Layer Security over standard port 443. More importantly, to prevent academic researchers and privacy advocates from easily inspecting what data is inside those packets, manufacturers aggressively employ TLS Certificate Pinning and mutual authentication hardcoded directly into the television’s read-only firmware.
In a standard enterprise environment, security teams inspect employee web traffic by deploying a Man-in-the-Middle decryption proxy at the firewall. This works on corporate laptops because the information technology department installs a trusted internal Root Certificate Authority onto every employee’s machine.
You cannot install a corporate Root Certificate Authority onto the locked bootloader of a consumer Samsung Tizen, LG webOS, or Hisense Vidaa television.
If an enterprise firewall attempts to intercept and decrypt the encrypted handshake coming from a Smart TV, the television’s pinned certificate check fails immediately. The television refuses the connection, breaks its cloud services, and throws incessant network error pop-ups across the conference room screen. Faced with angry executives complaining that the boardroom display will not cast or update right before a presentation, network administrators almost universally take the path of least resistance: they whitelist the television’s hardware address or bypass encryption inspection for audiovisual subnets.
“Because you cannot install an enterprise Root Certificate Authority or an endpoint detection agent onto a television’s locked firmware, security teams routinely whitelist the device — creating an encrypted, uninspected tunnel straight from the boardroom to an overseas server.”
Once encryption inspection is bypassed, the enterprise firewall is reduced to a blind traffic cop. All it sees is an encrypted packet of a few kilobytes leaving the building every sixty to ninety seconds, addressed to a legitimate, manufacturer-owned cloud domain hosted on Amazon Web Services, Akamai, or Alibaba Cloud. Because the Northeastern University researchers themselves noted that encrypted payloads prevent external observers from verifying whether opted-out televisions are sending benign keep-alive pings or compressed viewing hashes, a corporate security analyst staring at a monitoring dashboard has zero visibility into what is actually inside that stream.
Nor can you install an Endpoint Detection and Response agent like CrowdStrike Falcon, SentinelOne, or Microsoft Defender onto a television. The display sits on the network as an unmanaged, unpatchable black box — trusted by default simply because it is bolted to the drywall.
Nation-State Co-optation and the Weaponized Firmware Update
Even if we grant the most charitable assumption in the world — that television manufacturers only collect telemetry to sell detergent commercials and optimize screen brightness — the infrastructure they have built is a turnkey intelligence platform waiting to be co-opted.
When evaluating the risk of an always-on sensor inside a sensitive workspace, security architects must look at the digital supply chain and the legal jurisdiction of the vendor. Today’s flat-panel ecosystem is overwhelmingly concentrated in East Asia. Hisense and TCL, which together command nearly thirty percent of the global television market and a massive share of budget-friendly office displays, are headquartered in the People’s Republic of China — in Qingdao and Huizhou, respectively — with significant state-backed ownership structures. Samsung and LG are headquartered in South Korea, operating global cloud backends and sourcing critical system-on-chip silicon, wireless modules, and display sub-assemblies from fabrication plants spanning Taiwan, mainland China, and Vietnam. Sony and Sharp, headquartered in Japan — with Sharp majority-owned by Taiwanese electronics giant Foxconn — similarly rely on deeply intertwined Asian semiconductor and firmware development pipelines.
For hardware, software, or cloud infrastructure touching Chinese jurisdiction, the legal reality is unambiguous. Under Article 7 of China’s 2017 National Intelligence Law, reinforced by the 2021 Data Security Law and Counter-Espionage Law:
“All organizations and citizens shall support, assist, and cooperate with national intelligence efforts in accordance with law, and shall protect the secrets of national intelligence work of which they are aware.”
As legal scholars and supply chain risk analysts at SovereignSky and China Legal Experts have repeatedly emphasized, this is not an optional guideline. If the Ministry of State Security demands that a domestic manufacturer — or a domestic cloud subsidiary — hand over the device-graph telemetry of televisions operating inside a specific Internet Protocol range in San Francisco, Arlington, or London, the company is legally compelled to comply in secret. This exact statutory reality is why the Texas Attorney General’s lawsuit against Hisense and TCL elevated consumer ACR tracking from a deceptive trade practice to an explicit national security threat.
The “Weeping Angel” Precedent: When the TV Plays Dead
What happens when a nation-state decides that passive screen metadata and network maps are not enough, and wants raw, continuous audio from an executive boardroom?
They do not need to send a nervous engineer with a roll of toilet paper and a USB stick. They just need an Over-The-Air firmware update.
We do not have to speculate about whether intelligence agencies can convert consumer televisions into covert room bugs; we have had the receipts for nearly a decade. In March 2017, WikiLeaks published the “Vault 7” disclosures, exposing a top-secret joint program developed by the Central Intelligence Agency’s Embedded Devices Branch and the United Kingdom’s MI5 codenamed Weeping Angel.
As detailed in the leaked engineering manuals and reported by CBS News, Weeping Angel was designed specifically to infest Samsung Smart TVs. Once deployed, the implant hijacked the television’s power management subsystem to create a “Fake-Off” mode. When executives in the room pressed the power button on the remote at the end of a presentation, the television extinguished its front power indicator light and shut off the liquid-crystal display backlight, convincing everyone in the room that the television was completely powered down.
In reality, the television’s underlying processor and internal microphone remained fully energized. While sitting in Fake-Off mode, the television operated as a high-gain acoustic bug, recording every word spoken in the room, compressing the audio into local flash storage, and quietly transmitting the recordings over the internet to a covert intelligence server the moment the wireless interface initialized.
“In ‘Fake-Off’ mode, the television extinguishes its screen and power light so the room’s occupants believe it is dead — while the underlying processor and microphone array remain fully energized, recording every word spoken at the table.”
When Weeping Angel was originally engineered in 2014, intelligence operatives still needed physical access via a USB drive to downgrade and infect the television’s firmware, because automatic over-the-air update pipelines were still maturing. Today, in 2026, every Smart TV is architected to receive silent, automated firmware updates directly from the vendor’s cloud.
Because the vendor holds the private cryptographic signing keys for the television’s bootloader, a compromised vendor update server — or a vendor compelled by a state intelligence directive — can push a surgical firmware update targeted to a single television’s serial number or public IP address. That update is cryptographically valid. It passes through the corporate firewall over port 443 without raising a single alert. It alters the wake-word signal processor so that instead of waiting for a voice trigger like “Hey Google,” “Alexa,” or “Hi Bixby,” the microphone buffer streams continuously, packaging the room’s audio into the exact same sixty-second encrypted telemetry packets the firewall has been ignoring for years.
Even the Federal Bureau of Investigation knows this vector is wide open. As early as 2019, as reported by CE Pro, the FBI’s Portland Field Office issued a public cyber advisory warning that threat actors can hijack unsecured Smart TVs to commandeer their built-in cameras and microphones, explicitly advising users that if they cannot verify the firmware security of a display, they should resort to placing black tape over the sensors or pulling the power plug from the wall.
How the Trojan Horse Enters the Boardroom
If the surveillance capabilities of Smart TVs are documented in peer-reviewed computer science journals, prosecuted by State Attorneys General, and weaponized by intelligence agencies, why are consumer Smart TVs still hanging on the walls of Silicon Valley artificial intelligence labs, defense contractors, law firms, and Fortune 500 boardrooms?
Because of a classic organizational failure: the procurement gap between Facilities and Security Operations.
In almost every modern enterprise, laptops, servers, and mobile phones are procured by Information Technology under strict security governance. Before a new laptop touches the corporate network, it is imaged, enrolled in Mobile Device Management, hardened with disk encryption, and outfitted with endpoint detection sensors.
Conference room televisions, however, are rarely bought by the Chief Information Security Officer’s team. They are bought by Workplace Facilities, Office Managers, or third-party Audio/Visual integrators.
When an organization opens a new floor of executive offices or spins up an engineering war room, Facilities is told to put 75-inch or 85-inch screens in twelve conference rooms. An enterprise-grade, non-smart commercial monitor designed for secure environments costs between two thousand and four thousand five hundred dollars. Meanwhile, a consumer 85-inch TCL, Hisense, LG, or Samsung Smart TV is sitting on sale at Best Buy, Costco, or Amazon Business for under nine hundred dollars — subsidized specifically by the manufacturer’s Automatic Content Recognition surveillance revenue model.
Seeing an opportunity to save thirty thousand dollars on the office buildout budget, the facilities manager buys a dozen consumer Smart TVs on a corporate credit card. The audiovisual installer mounts them to the drywall, connects them to the office Wi-Fi so the smart home screen stops nagging for an internet connection, clicks “Agree” on the privacy policy, and walks out. The security team is never notified. The threat model is never updated. And just like that, an international surveillance appliance is given a front-row seat to the company’s crown jewels.
The Executive SecOps and Procurement Playbook: Closing the Blind Spot
Laughing at the OpenAI operative with his toilet-paper-wrapped USB microphone is easy. Auditing your own conference rooms takes discipline. If your organization handles proprietary artificial intelligence weights, trade secrets, merger and acquisition strategy, regulated financial data, or national security contracts, treating a conference room television as “just a monitor” is professional negligence.
Closing this blind spot requires a mandatory, defense-in-depth hardware and network posture enforced jointly by the Chief Information Security Officer, Network Engineering, and Corporate Procurement.
Step 1: Institute a Categorical Procurement Ban on Consumer Smart TVs
The cleanest way to eliminate consumer telemetry hardware is to stop buying consumer televisions for business environments. Corporate procurement policies must prohibit the purchase of any retail display containing a consumer Smart Operating System — including Tizen, webOS, Google TV, Roku OS, Fire TV, and Vidaa — or built-in voice-assistant microphones for use in executive offices, boardrooms, research labs, or collaboration spaces.
Instead, mandate commercial-grade, non-smart digital signage displays, often referred to in the industry as professional panels or tuner-free monitors. These displays are engineered for continuous enterprise operation, contain zero consumer advertising spyware, ship without far-field voice-assistant microphones, and support enterprise security protocols like 802.1X port authentication and Simple Network Management Protocol monitoring.
Two prominent enterprise baselines available through major commercial distributors include:
- Sharp NEC MultiSync M-Series and ME-Series: Commercial-grade, tuner-free 4K displays — such as the 65-inch PN-M652 and PN-ME652 distributed through CDW and ADI Global — built specifically for corporate presentation spaces without consumer tracking stacks or microphones.
- Planar UltraRes P Series and 21by9 Series: High-reliability commercial liquid-crystal displays engineered for secure command centers and executive boardrooms. Planar offers models with full Trade Agreements Act compliance for government and defense environments, alongside explicit certification under the European Telecommunications Standards Institute EN 303 645 cybersecurity standard.
Step 2: Enforce “Never-Connected” Air-Gapping for Existing Consumer Panels
If replacing existing consumer Smart TVs across every office is financially impractical in the current budget cycle, those displays must be subjected to a strict Zero-Network Air-Gap Protocol:
- Factory Reset to Revoke Permissions: Perform a full factory reset on every existing conference room Smart TV. During the initial setup wizard, skip all network configuration steps and explicitly decline all optional terms of service.
- No Wi-Fi, No Ethernet: A consumer Smart TV that has never been given wireless credentials or an Ethernet cable cannot establish an encrypted tunnel to an overseas server. Never connect the television itself to the corporate network.
- Disable SoftAP and Bluetooth Beacons: Enter the television’s hidden service menu — accessible via vendor-specific remote key sequences — and disable the internal Wi-Fi Direct access point radio and Bluetooth controller. Many unconfigured Smart TVs broadcast their own open Wi-Fi Direct networks or ultrasonic and Bluetooth Low Energy beacons, searching for nearby smartphones with companion apps installed to bridge their telemetry out to the internet.
Step 3: Hardware-Level Lobotomy for High-Security Enclaves
In executive boardrooms, war rooms, and frontier research spaces, software switches cannot be trusted; as the October 2026 Northeastern University study proved, opting out in software does not stop underlying firmware processes. Before a consumer or prosumer panel is hung in a sensitive room, hardware security technicians should open the rear chassis and perform a physical lobotomy:
- Unplug the Wireless Daughterboard: In virtually all modern flat-panel televisions, the Wi-Fi and Bluetooth radio is a discrete modular board connected to the main logic board via a standard ribbon cable. Physically remove the module.
- Disconnect Internal Microphones and USB Power Rails: Physically sever or unplug the internal microphone array ribbon near the bottom bezel. Furthermore — taking a direct lesson from the OpenAI espionage incident — disconnect or epoxy-seal unused rear USB ports so that an insider cannot use the television’s five-volt power rail to energize a parasitic recording device.
Step 4: Untrusted VLAN Segregation and DNS Sinkholing
In collaboration spaces where network connectivity is deemed operationally unavoidable — for example, to support native wireless screen-sharing protocols — the television must be treated as a hostile foreign endpoint:
- Dedicated Zero-Trust Audiovisual VLAN: Place all displays on a strictly segregated, non-routable virtual local area network. Configure firewall Access Control Lists to block all internal east-west traffic, preventing the television from using multicast protocols or address resolution scanning to discover employee laptops or internal servers.
- Default-Deny Egress and DNS Sinkholing: Block all outbound internet traffic from the audiovisual subnet to the open web. If selective cloud access is required, route all Domain Name System queries through an enterprise sinkhole — such as Cisco Umbrella, Cloudflare Gateway, or an internal Pi-hole cluster — configured to blackhole known manufacturer Automatic Content Recognition and telemetry domains across Samsung, LG, Hisense, TCL, Sony, and Vizio cloud infrastructures.
Step 5: Drive Pixels Exclusively via Managed Compute and TSCM Sweeps
Never use a television’s built-in processor to run conferencing software, web browsers, or document viewers. Treat the screen strictly as a dumb glass peripheral driven via HDMI from a dedicated, enterprise-managed compute unit — such as a locked-down Mac Mini, a Windows IoT Enterprise room system, or a FedRAMP-certified Cisco or Crestron conferencing codec — that runs your full corporate endpoint detection and encryption inspection stack.
Finally, expand your quarterly Technical Surveillance Countermeasures audits. Checking behind the television for a wad of toilet paper and a rogue USB stick is table stakes. Modern physical security teams must combine visual inspections with radio-frequency spectrum analyzers and network packet-capture taps to ensure the television itself is not the most sophisticated spy in the room.
The Real Lesson of San Francisco
When federal prosecutors present the photograph of Abdulrahman Alfozan peeking behind that San Francisco conference room television, the jury will see an open-and-shut case of old-fashioned corporate espionage. And rightly so — planting a covert microphone inside an employer’s executive suite is a brazen crime.
“We built digital fortresses around our server racks and air-gapped our AI model weights, only to hang the open ears and eyes of an international supply chain directly above the boardroom table.”
But for every Chief Information Security Officer, board member, and technology leader watching from the sidelines, the case should serve as a cold bucket of water. We have spent billions of dollars hardening our cloud perimeters, encrypting our databases, and training our employees not to click on phishing links. Yet we routinely invite multi-sensor, internet-connected computers engineered by foreign conglomerates into our most confidential rooms — handing them legal permission to watch our screens, listen to our voices, and map our networks in exchange for a thinner bezel and a cheaper price tag.
The spy behind the television was caught because he was an amateur who had to walk back into the room to fetch his data. The television he plugged his bug into never has to walk out the door. It sends its encrypted packets out through your firewall every sixty seconds — and until you pull the plug, it is still listening.
Works Cited and Further Reading
- OpenAI Engineer Arrested, Accused of Planting Listening Device Inside Company’s Office — CBC News / Thomson Reuters, accessed October 24, 2026, https://www.cbc.ca/news/world/open-ai-listening-device-fbi-9.7379357
- Ex-OpenAI Engineer Detained in Spy Device Case as Saudi Royal Contacts Emerge — The Hacker News, accessed October 24, 2026, https://thehackernews.com/2026/10/ex-openai-engineer-detained-in-spy.html
- Abdulrahman Alfozan, a Saudi National Employed as an Engineer at OpenAI, Caught on Hidden Camera Behind Conference Room TV — Reddit r/OpenAI Archive, accessed October 24, 2026, https://www.reddit.com/r/OpenAI/comments/1x5glxv/abdulrahman_alfozan_a_saudi_national_employed_as/
- Smart TV Privacy Study (“Watching the Watchers”) Finds Tracking Persists Even When Opting Out — Northeastern University / CyberInsider, accessed October 24, 2026, https://cyberinsider.com/smart-tv-privacy-study-finds-tracking-persists-even-when-opting-out/
- Samsung TVs Kept Tracking What People Watched Even After Users Turned Tracking Off, Study Finds — TechTimes UK, accessed October 24, 2026, https://www.techtimes.co.uk/samsung-tvs-kept-tracking-what-people-watched-even-after-users-turned-tracking-off-study-finds-1809347
- Your Smart TV is Watching What You Watch (ACR & HDMI Surveillance Research) — University of California, Davis / University College London / Universidad Carlos III de Madrid, accessed October 24, 2026, https://www.ucdavis.edu/news/your-smart-tv-watching-what-you-watch
- The Silent Watchers: How Smart TVs Invade Your Privacy Even When You’re Not Watching TV — United Nations University (UNU) Institute in Macau, accessed October 24, 2026, https://c3.unu.edu/blog/the-silent-watchers-how-smart-tvs-invade-your-privacy-even-when-youre-not-watching-tv
- Texas Attorney General Sues Multiple TV Makers Over ACR User Data Collection (Samsung, LG, Sony, Hisense, TCL) — Consumer Rights Wiki, accessed October 24, 2026, https://consumerrights.wiki/w/Texas_Attorney_General_sues_multiple_TV_makers_over_ACR_user_data_collection
- Your Smart TV May Be Watching You Back: Texas Reaches Privacy Settlement with LG Electronics — Fordham University Privacy Blog, accessed October 24, 2026, https://privacy.blog.fordham.edu/your-smart-tv-may-be-watching-you-back-texas-reaches-privacy-settlement-with-lg-electronics/
- Samsung TVs Stop Spying on Viewers in Texas: Here’s How to Disable ACR Anywhere — Malwarebytes Labs, accessed October 24, 2026, https://www.malwarebytes.com/blog/news/2026/03/samsung-tvs-stop-spying-on-viewers-in-texas-heres-how-to-disable-acr-anywhere
- Failure to Obtain Viewer Consent Leads to $2.2 Million Settlement for Vizio — Federal Trade Commission (FTC) / Retail & Consumer Products Law, accessed October 24, 2026, https://www.retailconsumerproductslaw.com/2017/02/failure-to-obtain-viewer-consent-leads-to-2-2-million-settlement-for-vizio/
- Vault 7: CIA Hacking Tools Revealed (“Weeping Angel” Samsung Smart TV Fake-Off Implant) — WikiLeaks, accessed October 24, 2026, https://wikileaks.org/ciav7p1/
- WikiLeaks Says CIA Hacked Samsung Smart TVs — CBS News, accessed October 24, 2026, https://www.cbsnews.com/news/cia-hacked-samsung-smart-tvs-wikileaks-vault-7/
- FBI Issues Warning on Smart TV Hacks and Unsecured Camera/Microphone Access — CE Pro / FBI Portland Field Office, accessed October 24, 2026, https://www.cepro.com/news/fbi-issues-warning-smart-tv-hacks/14709/
- National Intelligence Law of the People’s Republic of China (2017, Article 7 Supply Chain Mandate) — SovereignSky Supply Chain Risk Database, accessed October 24, 2026, https://sovereignsky.no/laws/national-intelligence-law/
- Chinese Intelligence Law: Article 7 Compliance and Corporate Obligations — China Legal Experts, accessed October 24, 2026, https://www.chinalegalexperts.com/news/chinese-intelligence-law-compliance-made-simple
- Sharp NEC MultiSync M2 Series 65" 4K UHD Commercial Tuner-Free Display (PN-M652) — CDW Enterprise Hardware, accessed October 24, 2026, https://www.cdw.com/product/nec-multisync-m2-series-65-led-backlit-lcd-display-4k-for-digital-si/8438749
- Sharp NEC MultiSync ME Series 65" Commercial Display (PN-ME652) — ADI Global Distribution, accessed October 24, 2026, https://www.adiglobaldistribution.us/product/1S-PNME652
- Planar 21by9 & UltraRes Series TAA-Compliant, ETSI EN 303 645 Cyber-Secure Commercial Displays — Planar Systems, accessed October 24, 2026, https://www.planar.com/products/large-format-lcd-displays/21by9-series/